Managed Security Services: What You Get for the Monthly Fee

Every few weeks, someone forwards me a proposal for managed security services with a version of the same question attached: what am I actually paying for? Usually, the quote has a tidy monthly number at the bottom, a page of acronyms above it, and almost nothing explaining how one connects to the other.
For context, I write for cybersecurity companies for a living. Over the years, I have drafted the service pages, pricing sheets, and sales decks that sit behind those proposals. On top of that, I have spent plenty of time on the other side of the table, helping operations and finance leaders decode them. So consider this the guide I wish more buyers had before their first discovery call: a plain explanation of what managed security services include, what they quietly leave out, and how to judge whether the monthly fee is fair.
What Managed Security Services Actually Are
In short, once you strip away the branding, managed security services come down to one arrangement. An outside team watches your environment, decides which signals matter, and acts on them, under a contract that spells out how fast and how far they will go. Typically, the provider is called an MSSP, short for managed security service provider.
However, this is not the same thing as your regular IT provider. A managed service provider keeps your systems running, whereas a managed security provider keeps those systems from being turned against you. Many IT providers do bundle some security into their plans, but the depth varies a lot. VC3 makes a useful point here: if you pay under $100 per user each month for managed IT, there is probably little meaningful cybersecurity included, perhaps some monitoring and alerts but not robust services or tools.
The key word, therefore, is “managed.” In other words, you are not buying software. Instead, you are buying people, process, and accountability, with the tools included as the means to deliver them. Keep that in mind, because it explains most of what follows.
Where the Managed Security Services Monthly Fee Goes
Whenever I build a service page for an MSSP, the features list always looks long. Underneath it, however, the fee funds a handful of core functions. Here is how they usually break down.
Round the Clock Monitoring and the SOC
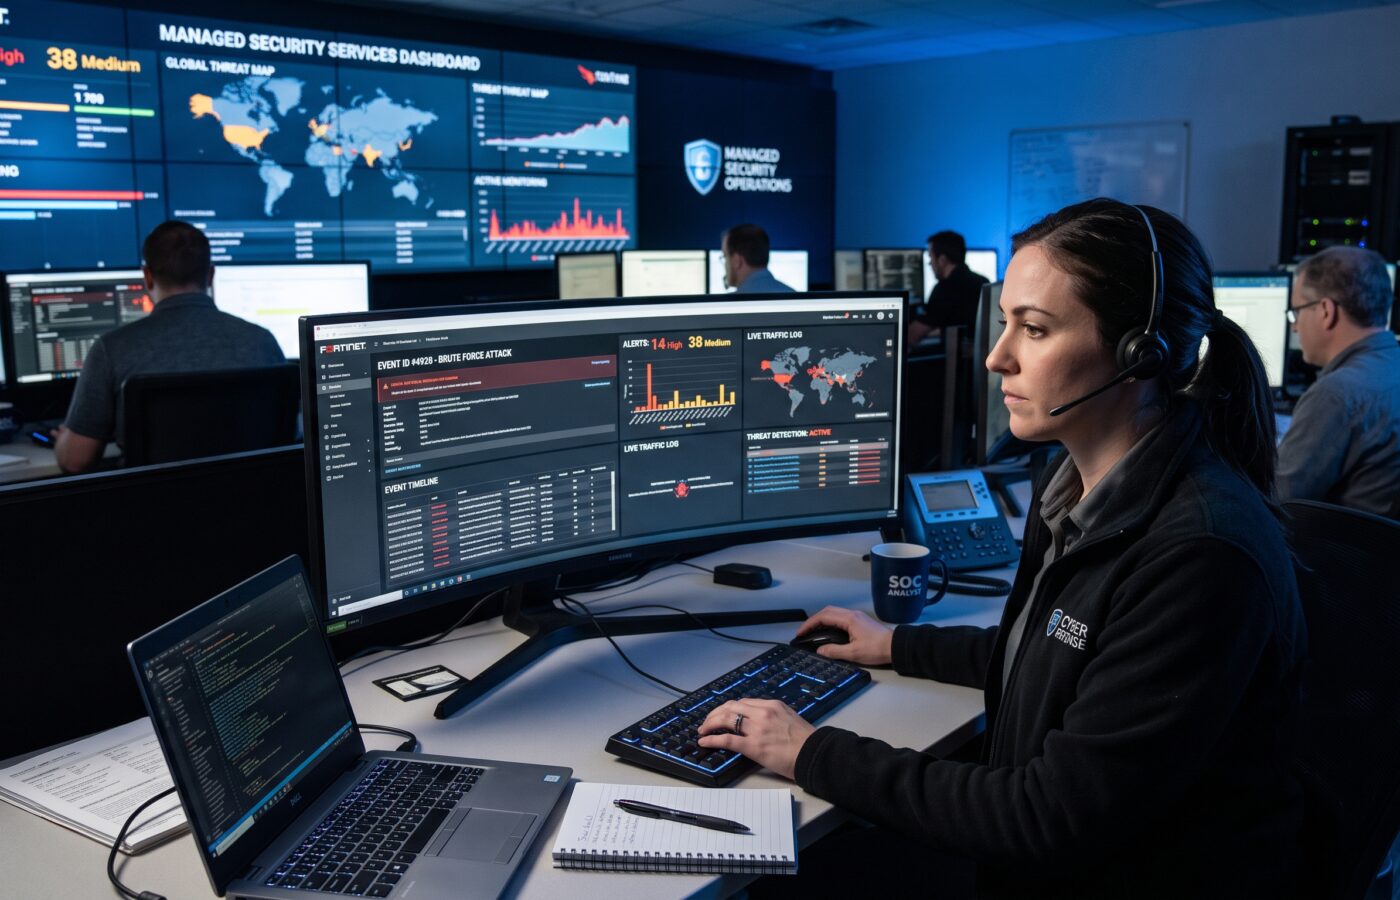
The biggest single cost inside managed security services is, quite simply, people watching alerts at 3 a.m. on a Sunday. That team sits in a security operations center, or SOC, and it is also the part of the service you would struggle most to replicate on your own.
So why does round the clock coverage matter so much? Because attackers do not keep office hours, and they move fast once they are in. For example, CrowdStrike’s 2026 Global Threat Report found that average eCrime breakout time dropped to 29 minutes in 2025, and the quickest breakout it observed took only 27 seconds. In this context, breakout time is the gap between an attacker getting a foothold and moving deeper into your network. As a result, if nobody is looking until Monday morning, that window has long since closed.
With that in mind, ask every provider one question: is the SOC staffed by your own employees, or is monitoring subcontracted to another firm? Neither answer is automatically wrong; still, you deserve to know who is actually looking at your data.
Managed Detection and Response
Monitoring tells you something is wrong. Response, on the other hand, does something about it. Managed detection and response, or MDR, is where the provider takes action on your behalf, for instance by isolating an infected laptop, disabling a compromised account, killing a malicious process, or blocking a suspicious connection.
That said, the detail that separates good contracts from weak ones is response authority. Some providers can only alert you and then wait for a callback. Others, by contrast, have preapproved permission to contain a threat immediately. Consequently, if your provider has to reach your IT manager before isolating a machine, and your IT manager is on a flight, the response time in the brochure means very little.
Endpoint, Email, and Identity Protection
In addition, most managed security services come bundled with the tools that generate the signals: endpoint detection and response agents on every laptop and server, email filtering to catch phishing and malicious attachments, and some form of identity protection such as multifactor authentication management. HDWebSoft describes the usual baseline as 24/7 threat monitoring, SOC access, MDR, endpoint protection, log management, vulnerability scanning, and cloud security. If your workloads sit in AWS or Azure, confirm that the cloud security piece actually supports your platform natively.
Before signing, ask whose name the licenses are under. If the tooling belongs to the provider, then leaving them later means ripping out and replacing every agent in your environment. Of course, that is not a reason to walk away, but it should factor into how you negotiate contract length.
Vulnerability Management and Patching
Lately, this one has become much more important. According to Verizon’s 2026 Data Breach Investigations Report, exploiting software flaws, at 31% of breaches, overtook stolen credentials as the leading way in for the first time. In other words, unpatched systems are now the front door.
Unfortunately, there is a trap I see in proposals constantly, because “vulnerability management” can mean two very different things. Some providers scan your systems and send a report listing what is broken. Others, meanwhile, actually apply the patches and verify they took. The first is a to do list, while the second is a service. Therefore, find out which one you are buying.
Keep in mind, too, that scanning is not the same as testing. A scan flags known weaknesses, while a pen test proves what an attacker could actually exploit, so budget for both (our guide to penetration testing cost covers the numbers). And if you run custom built applications, fixing flaws in that code usually falls to your developers rather than your MSSP, which is worth factoring into your custom software development cost.
Log Management and SIEM
Every device in your network generates logs. A security information and event management platform, or SIEM, collects them, correlates them, and stores them so analysts can spot patterns and investigate incidents after the fact.
There are two things to check here. First, consider retention: how long are your logs kept? Many compliance frameworks and cyber insurers expect a set period, and besides, an investigation into an incident that started months ago needs logs from months ago. Second, look at volume, since some providers price SIEM by how much data you send, which can make the bill climb as your business grows.
Compliance Support and Reporting
Most providers also deliver monthly reports summarizing alerts, incidents, and the overall state of your security. Better ones, moreover, help produce evidence for audits and for the security questionnaires that cyber insurers and enterprise customers now send out routinely. Many packages likewise include compliance support for frameworks such as HIPAA, PCI DSS, and NIST. So if your business answers to any of those, confirm the report formats actually match what your auditor wants to see.
Security Awareness Training
Finally, many packages include phishing simulations and short training modules for staff. Admittedly, it can feel like a box ticking exercise, but the data says otherwise. Verizon found that 62% of breaches involved the human element, with social engineering ranking as the third most common breach pattern. What’s more, the target is shifting: attackers are moving to mobile devices, where people tend to fall for fake texts and scam calls more readily than for traditional email phishing. Therefore, if your training still only covers email, it is behind.
What Managed Security Services Usually Do Not Cover
This is the section most buyers skip, and yet it causes the most arguments later. In my experience, people often discover the exclusions in the middle of an incident, which is the worst possible time.
Full incident remediation. Containing a threat is usually included. Cleaning up afterward, however, along with rebuilding servers and restoring data, often is not. Corsica Technologies notes plainly that most MSSPs charge extra for incident remediation. For that reason, ask for the hourly rate or retainer terms in writing before you need them.
Forensics, legal, and breach notification. Similarly, a serious breach can require forensic investigators, outside counsel, and customer notification. These are typically separate engagements, and they are sometimes arranged through your cyber insurer.
Onboarding and setup. Deploying agents, connecting log sources, and tuning alerts takes real work. As a result, initial setup, integrations, and log ingestion configuration can run several thousand dollars or more in complex environments.
Projects. Likewise, replacing a firewall, migrating to a new cloud platform, or redesigning your network counts as project work, not monthly service.
Your vendors’ security. Finally, your provider watches your environment, not your suppliers’. That gap matters more every year; in fact, Verizon reported that breaches involving an organization’s supply chain rose 60%, and third parties now appear in 48% of breaches. That includes outsourced development partners, so weigh their security practices alongside the numbers in our software development outsourcing cost guide. Therefore, ask whether vendor risk reviews are in scope or available as an add on.
How Managed Security Services Are Priced
There are four common pricing models, and most providers use some blend of them.
The Four Common Pricing Models
Per device. Under this model, you pay a set monthly rate for each laptop, server, or virtual machine under protection. Huntress gives a useful sense of the spread: basic tiers might run $8 to $12 per device monthly, while premium tiers with advanced threat hunting and incident response can reach $20 to $30 per device.
Per user. Here, the charge is for each employee or account, regardless of how many devices they use. Because of this, it suits businesses where people work across a laptop, a phone, and a tablet.
Tiered packages. Think bronze, silver, and gold, or some variation. Generally, lower tiers cover monitoring and alerting, whereas higher tiers add response, threat hunting, and compliance support.
Flat rate. One fixed number covers a defined scope. It is easy to budget; even so, read the scope boundaries carefully.
What Managed Security Services Cost Per Month
So what does it add up to? For smaller organizations, MSSP Providers suggests a planning range of $2,000 to $7,000 a month, while broader midsize programs may plan around $7,000 to $25,000. Likewise, VC3 puts the floor in a similar place, noting that outsourced cybersecurity services typically start at a minimum of $2,000 to $3,500 per month.
To illustrate, here is a quick worked example. Say you have 60 staff and 80 protected devices, and you choose a premium per device tier at $25. In that case, the bill comes to $2,000 a month before onboarding, log volume charges, or any add ons. If you run your own numbers this way, you will spot inflated quotes quickly.
Why Managed Security Services Look Expensive Until You Price the Alternative
When finance teams push back on the cost of managed security services, the comparison they usually have in mind is zero. In reality, the true comparison is doing it yourself, or dealing with a breach.
The Cost of Building It In House
Round the clock coverage means shifts, and shifts, in turn, mean headcount. Providing 24/7 monitoring typically takes at least five to six analysts plus management, tooling, and infrastructure, and the total cost of an internal SOC can exceed $700,000 per year. On top of that, those people are hard to find. The 2025 ISC2 Cybersecurity Workforce Study found that 88% of respondents had experienced at least one significant cybersecurity consequence because of a skills shortage, and 69% had experienced more than one. Furthermore, a third said their organizations lacked the resources to staff their teams adequately. The same math applies to IT more broadly, as our managed IT services vs in-house cost comparison shows.
The Cost of Absorbing a Breach
Meanwhile, IBM’s Cost of a Data Breach Report 2026, published in July, puts the global average at $4.99 million, a record and 12% higher than the year before, with the US average reaching $11.5 million. Speed, moreover, is a big part of that number. Breaches that ran longer than 200 days averaged $5.65 million, compared with $4.32 million for those resolved faster. At the same time, the mean time to identify and contain a breach rose to 247 days, ending five consecutive years of decline.
Smaller firms, therefore, should not assume they are below the radar. Verizon’s 2025 DBIR found that among small and midsize businesses, ransomware was involved in as much as 88% of breaches studied. Attackers target smaller companies precisely because they tend to have fewer people watching.
What Managed Security Services Can and Cannot Promise
Even so, I want to be honest about one thing. Managed security services are not a guarantee. No provider can make you breach proof, and any salesperson who implies otherwise is overselling. Ultimately, what you are really paying for is speed: shrinking the time between something going wrong and someone competent doing something about it. Given the numbers above, speed is exactly where the money is saved.
Questions to Ask Before You Sign
Before you sign, bring this list to every provider conversation. After all, the answers will tell you more than any slide deck.
- What are your response time commitments, and are they in the contract? Get the actual service level agreement, not a marketing promise.
- Which actions can you take without calling us first? Ideally, clarify preapproved containment actions in writing.
- Who staffs the SOC, and where? Specifically, ask whether it is in house or subcontracted, and in which time zones.
- Does vulnerability management include patching, or just scanning?
- What is excluded, and what does it cost when we need it? Also, ask for incident response rates and retainer terms now.
- How long are logs retained, and is storage priced by volume?
- Who owns the tool licenses, and what happens when we leave? In particular, ask about data export and offboarding support.
- Can we see a sample monthly report? If the report is just a list of blocked threats with no context or recommendations, that tells you how much thinking goes into the service.
Red Flags in Managed Security Services Proposals
After years of reading these proposals, I have noticed a few patterns that make me cautious every time.
Vague scope. For example, phrases like “comprehensive protection” without a defined list of covered systems, response actions, and exclusions.
No mention of response authority. If a proposal talks endlessly about detection but barely mentions what happens next, then the service probably stops at sending you an email.
Pricing that seems too good. Remember the VC3 benchmark, because very cheap security bundled into a basic IT plan usually means alerting, not defending.
Long lock in with no exit terms. Admittedly, a three year contract can be reasonable for pricing stability, but only with clear offboarding and data handover commitments.
Guarantees of zero breaches. Simply put, nobody can promise this. Consequently, a provider that does is either naive or not being straight with you.
So, Are Managed Security Services Worth the Monthly Fee?
For most small and midsize businesses, the honest answer is yes, provided you know what you are buying. After all, managed security services give you a team you could not realistically hire, tools you would otherwise license and maintain yourself, and around the clock attention at a predictable monthly cost.
However, the value falls apart when the scope is unclear. So pay for response, not just alerts. Next, get the exclusions in writing. Above all, know who is watching and what they are allowed to do. Once you do that, the monthly fee stops being an abstract line item and becomes what it should be: the cost of making sure that when something goes wrong, someone notices in minutes rather than months.
Frequently Asked Questions
What is included in managed security services?
Most packages include round the clock monitoring through a SOC, managed detection and response, endpoint and email protection, vulnerability scanning, log management, and compliance reporting. In addition, higher tiers add threat hunting and deeper incident response. See HDWebSoft for a typical baseline.
How much do managed security services cost per month?
Small organizations commonly budget $2,000 to $7,000 a month, while midsize programs often run $7,000 to $25,000. Per device rates, meanwhile, range from roughly $8 to $30 depending on tier. See MSSP Providers and Huntress.
What is the difference between an MSP and an MSSP?
An MSP manages and supports your IT systems day to day. An MSSP, by contrast, focuses specifically on detecting and responding to security threats. Many MSPs include basic security, but usually not at the depth a dedicated MSSP provides. See VC3.
Is incident response included in the monthly fee?
Initial containment usually is. However, full remediation, recovery, and forensics are often billed separately, so always confirm in writing. See Corsica Technologies.
Are there setup or onboarding fees?
Often, yes. Deploying agents, connecting log sources, and configuring integrations can cost several thousand dollars in complex environments. See MSSP Providers.
Do small businesses really need managed security services?
In most cases, yes. Small businesses are heavily targeted, particularly by ransomware, because they tend to have fewer defenses and less monitoring. See Barr Advisory.
References
- Help Net Security. “Data breach cost 2026 averaged $4.99 million, AI attacks ran higher.” helpnetsecurity.com
- Compliance Docs HQ. “Data Breach Cost Statistics (2026).” compliancedocshq.com
- Cyberdise. “Data Breach Costs 2026: $4.99M and 247 Days to Detect.” cyberdise-awareness.com
- Verizon. “2026 Data Breach Investigations Report.” verizon.com
- Verizon News. “Vulnerability exploitation top breach entry point, 2026 industry wide DBIR finds.” verizon.com
- Help Net Security. “Lessons for organizations from the Verizon 2026 Data Breach Investigations Report.” helpnetsecurity.com
- Security Magazine. “Strategies, Expert Insights from the 2026 Verizon DBIR.” securitymagazine.com
- Barr Advisory. “3 Key Takeaways from the 2025 Verizon DBIR.” barradvisory.com
- CrowdStrike. “2026 Global Threat Report: AI Accelerates Adversaries and Reshapes the Attack Surface.” crowdstrike.com
- ISC2. “ISC2 Study Finds Cybersecurity Budget Constraints Remain, But Do Not Worsen, While Skill Needs Grow.” isc2.org
- Cybersecurity Stats. “2025 ISC2 Cybersecurity Workforce Study.” cybersecuritystats.com
- Huntress. “How to Calculate Managed Security Service Cost Per Device.” huntress.com
- VC3. “How Much Do Managed Cybersecurity Services Cost?” vc3.com
- Corsica Technologies. “Managed Security Services Pricing: Getting the Best Value.” corsicatech.com
- MSSP Providers. “Managed Security Services Pricing 2026.” msspproviders.io
- MSSP Providers. “How Much Does an MSSP Cost in 2026?” msspproviders.io
- HDWebSoft. “Managed Security Service Pricing: What You Actually Pay and Why It Matters.” hdwebsoft.com