Every few weeks, a CEO or managing partner forwards me a vendor proposal for managed detection and response, or one of its close cousins, with the same note on top: “Do we need this?”
The proposal usually has three acronyms in it, a price per endpoint, and a slide promising the product stops nearly every attack known to humankind. Sometimes it’s EDR. Sometimes it’s XDR. More and more often, it’s MDR, pitched as the thing that finally makes security somebody else’s problem.
I work as a fractional CISO. In practice that means I hold the security leadership seat for several organizations at once: an accounting firm, a staffing agency, a software consultancy, and a handful of professional services companies that grew faster than their IT budgets did. None of them run a security operations center. Most have one or two IT people who are already juggling help desk tickets, laptop refreshes, Microsoft 365 licensing and a conference room display that refuses to cooperate. So when they ask me which acronym they need, I’m not answering in theory. I’m answering with their payroll, their insurance renewal and their actual people in mind.
This is the answer I give them. I’m writing it down so I can stop repeating it in meetings.
EDR, XDR and Managed Detection and Response: The Short Version
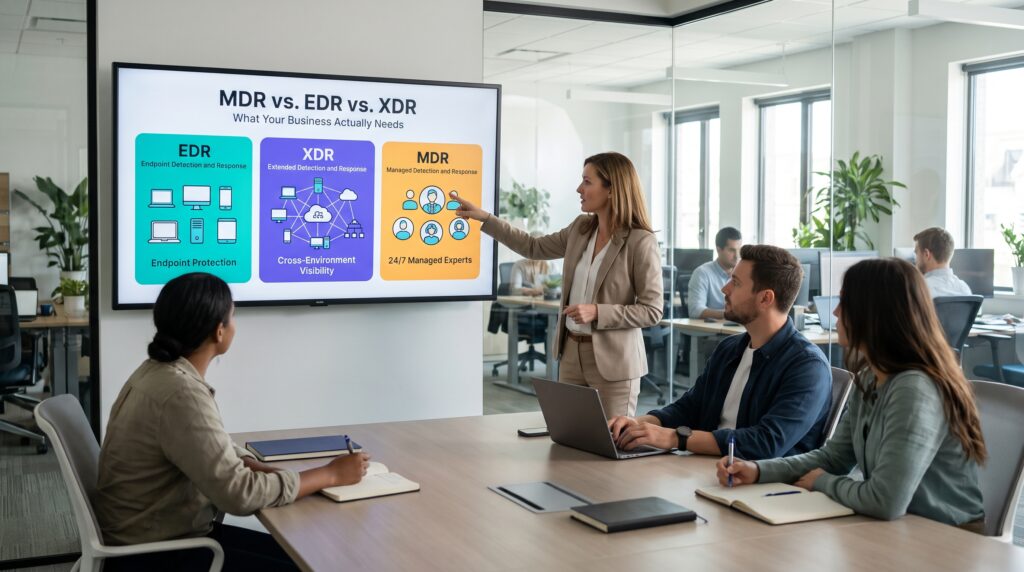
EDR is a tool. It watches your laptops and servers, records what happens on them, and gives someone the ability to kill a malicious process or cut a machine off the network.
XDR is a bigger tool. It pulls signals from endpoints, email, identity, cloud apps and network gear into one place, so an analyst sees a single attack instead of forty unrelated alerts.
MDR is people. It’s a team outside your company that watches whatever tools you have, around the clock, and takes action when something is wrong.
Here’s the part vendors tend to blur. EDR and XDR are things you own. Managed detection and response is a decision about who actually uses those things at 2:47 on a Sunday morning. For most businesses under roughly a thousand employees, that second question matters far more than which dashboard you buy.
Now let me unpack each one properly, because the details are where budgets get wasted.
What EDR Really Does (and What It Doesn’t)
Endpoint detection and response replaced the old idea of antivirus. Traditional antivirus compared files against a list of known bad signatures. If the malware was new, or if the attacker didn’t use malware at all, antivirus shrugged.
EDR watches behavior instead. It notices when Word suddenly launches PowerShell, when a user account starts encrypting hundreds of files in a minute, or when a process tries to dump passwords from memory. It keeps a running record of activity on each device, so an investigator can rewind the tape and see exactly how an intrusion unfolded. And it gives you response levers: isolate the host, kill the process, quarantine the file, sometimes roll back changes.
That’s genuinely valuable. It’s also why cyber insurers now treat EDR as table stakes. Insurers have been tightening their applications for years, and endpoint protection with behavioral detection is one of the first cyber insurance requirements they ask about, as Acronis explains in its breakdown of insurance qualification.
But here’s what I find when I walk into a new client’s environment, more often than I’d like to admit: a perfectly capable EDR product that nobody is looking at. The console has hundreds of unread alerts. Most were noise. A few weren’t. The tool did its job and raised its hand. There was simply nobody in the room to call on it.
EDR doesn’t watch itself. That’s the single most important sentence in this article.
It also only sees endpoints. If an attacker logs into your Microsoft 365 tenant with a stolen password and starts setting up mail forwarding rules to siphon invoices, there may be no laptop involved at all. Your EDR can be flawless and still miss the whole thing.
What XDR Adds on Top
Extended detection and response grew directly out of EDR. Forrester describes it as the evolution of EDR, with endpoint detections remaining the anchor while the platform folds in telemetry from email security, identity systems, network tools and cloud services. Gartner frames XDR as a unified detection and response platform that collects and correlates data from multiple security components, a definition summarized well in Kaseya’s XDR guide.
Why does that matter to a business owner? Because modern attacks rarely stay in one lane. The 2025 Sophos Active Adversary Report found that in 56 percent of the incident response and MDR cases it studied, attackers simply logged in with valid credentials rather than breaking in. A login from an unusual country, followed by a new inbox rule, followed by a file download on a laptop an hour later: each of those events looks minor alone. Together, they tell a story. XDR is built to connect those dots.
You’ll hear two flavors. Native XDR comes from a single vendor whose own products feed the platform. Open or hybrid XDR ingests data from tools you already own, from different vendors, through integrations. Sophos lays out the distinction clearly in its XDR common questions page. Native tends to be tighter and simpler. Open protects the investments you’ve already made. Neither is wrong.
My caution with XDR is simple. It produces more signal. More signal with no one to interpret it just means more unread alerts in a fancier console. I’ve seen companies upgrade from EDR to XDR expecting to feel safer and end up feeling more overwhelmed. The platform works. The staffing model didn’t change.
Managed Detection and Response Is a Service, Not a Product
This is where most of the confusion lives.
Gartner defines managed detection and response services as providers that deliver security operations center functions remotely to their customers. Its market guide expects 24/7 staffing, analysts who engage with each customer’s own data, and providers that triage, investigate and manage the response to discovered threats. You can see the category and the providers Gartner tracks on its MDR reviews and ratings page, and the 2024 Gartner Market Guide for Managed Detection and Response goes further, predicting that by 2028 half of MDR findings will focus on or include detail about threat exposures, compared with roughly a tenth at the time of writing.
Notice what’s missing from that definition: a specific technology. A good MDR provider runs on top of EDR or XDR, either theirs or yours. The tooling is the instrument. The provider is the musician.
Watch Out for Managed Detection and Response in Name Only
That distinction protects you from a common trick. Gartner has flagged a growing number of technology-centric offerings that carry the MDR label while delivering little real human analysis, a trend eSentire summarized from the 2024 market guide. In plain terms, some vendors bolt a monitoring fee onto their software and call it managed detection and response. If the “service” amounts to automated emails that say “we detected something, please investigate,” you bought a notification system, not a security team.
Notify-Only Versus Hands-On Response
Real managed detection and response comes in two shapes, and you need to know which one you’re signing:
- Notify and advise. The provider investigates, confirms the threat, then calls or messages your team with recommended actions. Your people do the containment.
- Hands-on response. The provider has authority, agreed in advance, to isolate machines, disable accounts, revoke sessions and kill processes on your behalf, then tells you what they did.
For a company with no overnight IT coverage, option one is barely better than nothing. If the alert arrives at 3 a.m. and the person who can act is asleep until 7, the attacker has four free hours.
Why Managed Detection and Response Comes Down to the Clock
Let me show you the numbers that changed how I advise clients.
Attackers move fast once they’re inside. Sophos found the median time between an attacker’s first action and their first attempt to compromise Active Directory, the system that controls nearly every user and computer in a typical Windows environment, was about 11 hours. The same report found that 83 percent of ransomware payloads were deployed outside normal business hours. That is not a coincidence. Criminals know when your office is empty.
Now compare detection speed. In the Sophos data, median dwell time in MDR cases was three days for ransomware attacks and one day for everything else. In cases where the victim called in incident responders after the fact, dwell time was four days for ransomware and eleven and a half days for other intrusions. Same threat landscape. Very different outcomes, depending on whether someone was actively watching.
What Mandiant and IBM Found
Mandiant’s research points the same way. In its M-Trends 2026 Executive Edition, Mandiant reported that global median dwell time climbed to 14 days, up from 11 the previous year, driven largely by espionage groups and insiders who prioritize staying hidden. Coverage of the report noted that the handoff from initial access to a secondary threat group collapsed to a matter of seconds in some cases, a detail Decryption Digest broke down in its analysis.
The cost side is just as blunt. IBM’s 2025 Cost of a Data Breach research put the global average breach at USD 4.44 million, with a mean lifecycle of 241 days to identify and contain. Organizations using security AI and automation extensively cut that lifecycle by about 80 days and saved roughly USD 1.9 million, as Infosecurity Magazine reported.
Why Smaller Businesses Feel It Most
If you run a smaller business, the Verizon 2025 DBIR SMB snapshot is the page to read. Ransomware appeared in 88 percent of breaches at small and medium businesses, compared with 39 percent at larger organizations, according to Infosecurity Magazine’s coverage of the findings.
Put those together and the conclusion is uncomfortable but clear. Speed is not mainly a technology problem. It’s a staffing problem. The best EDR in the world raises its alert in seconds. What decides whether you lose a laptop or lose the company is how long that alert sits before a qualified human acts on it.
Five Questions to Ask Before Buying Managed Detection and Response
When a client asks me “EDR, XDR or MDR?”, I don’t answer directly. I ask these five questions first.
1. Who Answers an Alert at Night, on Weekends and During Holidays?
If the honest answer is “nobody” or “our MSP, eventually,” you need managed detection and response, full stop. Owning a better tool without fixing this gap is buying a louder smoke alarm for an empty house.
2. What Does “Response” Mean in Writing?
I want the contract to name the specific actions the provider can take without calling us first, the response time commitments for each severity level, and who on our side gets the call when something escalates. If those details are vague in the sales stage, they’ll be worse during an incident.
3. Where Do Your Incidents Actually Start?
For most of my professional services clients, the front door is email and identity, not a laptop. Phishing, stolen passwords, MFA fatigue, malicious OAuth apps. If your MDR provider only watches endpoints, you’re defending the back door while the front one stands open. That’s the strongest practical argument for XDR telemetry underneath your MDR service.
4. What Do Your Insurer and Your Clients Demand?
Cyber insurance applications increasingly ask about EDR, continuous monitoring and an incident response plan. Your larger clients may send security questionnaires asking the same. Sometimes the right purchase is the one that lets you answer “yes” honestly to the questions that keep revenue flowing.
5. What Can You Realistically Staff Yourself?
Covering one seat around the clock takes far more than one hire. A week has 168 hours. A full-time analyst works about 40 of them. Add vacations, sick days, training and turnover, and you need something like five or six qualified people just to keep one chair warm all the time. For most companies below enterprise size, that math ends the “build our own SOC” conversation quickly, for the same reasons it drives most managed IT versus in-house decisions.
Managed Detection and Response for Three Typical Businesses
Every environment is different, but most of my clients fall into one of three patterns.
The 20- to 75-Person Firm on Microsoft 365 With an Outsourced IT Provider
This is the most common profile I see in accounting, legal support, marketing agencies and consulting. Many business Microsoft licenses already include a capable EDR, so you may own the tool without realizing it. What’s missing is someone watching it, and your outsourced IT provider usually isn’t staffed to do that overnight. I usually recommend an MDR service layered over the existing stack, with explicit coverage for identity and email, not just devices. Spending on a brand-new XDR platform here is usually premature.
The 150- to 500-Person Company With a Small Internal IT Team
These organizations have more cloud apps, more remote staff, more vendors with access and more data worth stealing. Here I want managed detection and response built on XDR-style visibility: endpoint, identity, email and the major SaaS platforms feeding one investigation view. The internal team handles hygiene and business context. The provider handles the 24/7 watch and first response.
The 800-Plus Organization With a Dedicated Security Person or Two
At this size, owning an XDR platform starts to make sense because your team can tune it, hunt in it and build detections specific to your business. Many companies here use a co-managed MDR arrangement: internal staff during the day, the provider covering nights, weekends and surge capacity. The provider becomes an extension of the team rather than a replacement for it.
Notice that in all three cases, the recommendation starts with “who is watching” and only then moves to “what are they watching with.”
Red Flags When Shopping for Managed Detection and Response
I’ve sat through a lot of MDR sales presentations. These are the warning signs that make me slow down a deal:
- They can’t tell you who is on shift. A credible provider will explain where its analysts are, how shifts work and how many customers each analyst supports.
- Response means an email. If containment requires your team to log in and act, ask what happens when nobody responds for six hours.
- They only watch endpoints. Ask directly whether identity, email and cloud platforms are in scope, and what extra it costs.
- They insist on ripping out tools you already like. Sometimes consolidation is the right call. Sometimes it’s just a sales quota.
- Their reports count alerts instead of outcomes. “We processed 14,000 events” means nothing. “We contained two account takeovers and closed three exposed admin portals” means something.
- No onboarding or tuning period. The first 30 to 60 days should involve learning your environment, suppressing noise and agreeing on runbooks. If they promise full value on day one, be skeptical.
- No exit plan. Make sure you own your data and your logs, and that you can leave without losing your detection history.
Where a vCISO Fits Alongside Managed Detection and Response
I’ll be honest about a limitation of my own industry here. Managed detection and response is excellent at what it does, but it doesn’t run your security program. It won’t decide whether your CFO’s laptop gets isolated in the middle of month-end close. It won’t write your incident response plan, train your executives through a tabletop exercise, negotiate your insurance questionnaire or tell your board whether last quarter’s risk went up or down.
The NIST Cybersecurity Framework 2.0 organizes security into six functions: Govern, Identify, Protect, Detect, Respond and Recover. An MDR provider delivers a large part of Detect and a meaningful slice of Respond. Bitdefender makes a fair point in its guide to the NIST Detect and Respond functions: the two really belong together, because one is useless without the other. But that still leaves Govern, Identify, Protect and Recover sitting with you, alongside the wider technology roadmap a virtual CIO typically owns.
That’s the gap a virtual or fractional CISO fills. In my client work, the monthly rhythm usually looks like this. The MDR provider sends its report. I read it with the client’s IT lead, translate it into business risk, push back on the provider when something looks off, and decide which findings deserve budget. We keep the escalation list current. We test the response plan at least once a year. And when the provider calls at 3 a.m. asking for permission to disable the controller’s account, there’s already a documented answer.
The tool detects. The provider responds. Someone still has to own the decisions.
So, What Does Your Business Actually Need?
If you take one thing from this article, take this: stop comparing EDR, XDR and MDR as if they were three competing products on a shelf. They’re layers.
You need EDR, because every insurer, auditor and serious client will expect it, and because it’s the foundation everything else stands on.
You probably benefit from XDR-style visibility, because the attacks hitting businesses like yours start in email and identity far more often than they start on a laptop.
And unless you have people awake and qualified around the clock, you need managed detection and response, because the difference between a scare and a catastrophe is almost always measured in hours.
Buy in that order of thinking, not in the order a vendor’s slide deck presents it. And before you sign anything, make sure someone on your side, whether it’s an internal security lead or a fractional CISO, understands exactly what you’re getting and what you’re still responsible for.
Frequently Asked Questions
Is managed detection and response the same as a managed security service provider (MSSP)?
Not quite. Traditional MSSPs often focus on managing devices like firewalls and forwarding alerts, while MDR providers focus on investigating threats and actively responding to them. Gartner treats MDR as its own category, which you can explore on its MDR market page.
Do I still need EDR if I buy an MDR service?
Yes. MDR providers need telemetry to work with, and endpoint visibility is almost always part of that. Many providers either bundle their own EDR or run on top of the one you already own. Insurers also expect EDR on your devices, as Acronis outlines.
Is XDR worth it for a small business?
On its own, often not, because it generates more alerts than a small team can handle. Delivered through an MDR provider that uses XDR telemetry, it can be very worthwhile. Sophos notes that XDR is often consumed as a managed service by organizations with smaller security teams in its XDR FAQ.
How fast should an MDR provider respond to a critical threat?
Look for written commitments measured in minutes for critical incidents, along with clear authority to contain threats without waiting for your approval. The 2025 Sophos Active Adversary Report shows attackers attempting to compromise Active Directory within about 11 hours, so slow responses carry real risk.
Will managed detection and response lower my cyber insurance premium?
It can help, but no provider can promise a specific discount. What MDR reliably does is help you answer underwriting questions about continuous monitoring and incident response truthfully, which can affect eligibility, limits and pricing. Review your carrier’s actual application before assuming any savings.
Can my current IT provider deliver managed detection and response?
Some can, usually by partnering with a dedicated MDR vendor behind the scenes. Ask who actually staffs the overnight shift, what actions they can take on their own, and whether identity and cloud platforms are covered. If the answers are vague, the service probably is too, and it may be time to choose a managed service provider with a stronger security bench.
How do I know if a managed detection and response offering is real?
Ask for a sample incident report, a named escalation process and a description of analyst staffing. Gartner has warned about software products relabeled as MDR without meaningful human analysis, a concern eSentire summarizes here.
References
- Gartner. Market Guide for Managed Detection and Response (2024)
- Gartner Peer Insights. Managed Detection and Response Services Reviews and Ratings
- eSentire. What Is the MDR Gartner Magic Quadrant and Market Guide?
- Sophos. It Takes Two: The 2025 Sophos Active Adversary Report
- Mandiant (Google Cloud). M-Trends 2026 Executive Edition
- Decryption Digest. Mandiant M-Trends 2026: Ransomware Breakout Time Analysis
- Infosecurity Magazine. Data Breach Costs Fall for First Time in Five Years
- Verizon. 2025 Data Breach Investigations Report: Small- and Medium-Sized Business Snapshot
- Infosecurity Magazine. Verizon DBIR: Small Businesses Bearing the Brunt of Ransomware Attacks
- Forrester. XDR Defined: Giving Meaning to Extended Detection and Response
- Kaseya. What Is XDR? A Guide to Extended Detection and Response
- Sophos. What Is Extended Detection and Response (XDR)? Common Questions Answered
- Acronis. Why EDR Is Fundamental to Qualifying for Cyber Insurance
- National Institute of Standards and Technology. NIST Cybersecurity Framework
- Bitdefender. How to Use NIST CSF 2.0 to Identify Security Gaps: Detect and Respond